ayarema
Associate II
October 12, 2017
Solved

STM32F767ZI Nucleo : Cryptographic Library AES CBC Decryption Wrong Plaintext

  • October 12, 2017
  • 7 replies
  • 1594 views
Posted on October 12, 2017 at 23:55

Hardware and Software Versions:

MCU: STM32F767ZI Nucleo Board

En X Cube CryptoLib V3.1.0

Cube MX Version 4.22.1

Latest System Workbench 6 installation.

Problem:

Using AES 256 in CBC mode attempting to encrypt block of data on the Host which is the PC, and decrypt that same block on the MCU using the CryptoLib. Encryption on host is done correctly, decryption of the first block of data is done correctly on the MCU, but decryption of the second block of data fails(Bytes 16-31). Below is my test code.

uint8_t KeyTemp[32];

uint8_t KeyIvTemp[16];

uint8_t DataRaw[32];

uint8_t DataEncrypted[32];

for(int i = 0; i < 32; i++)

{

KeyTemp[i] = (uint8_t)i;

DataRaw[i] = 0;

}

for(int i = 0; i < 16; i++)

{

KeyIvTemp[i] = (uint8_t)i;

}

DataEncrypted[0] = 242;

DataEncrypted[1] = 144;

DataEncrypted[2] = 0;

DataEncrypted[3] = 182;

DataEncrypted[4] = 42;

DataEncrypted[5] = 73;

DataEncrypted[6] = 159;

DataEncrypted[7] = 208;

DataEncrypted[8] = 169;

DataEncrypted[9] = 243;

DataEncrypted[10] = 154;

DataEncrypted[11] = 106;

DataEncrypted[12] = 221;

DataEncrypted[13] = 46;

DataEncrypted[14] = 119;

DataEncrypted[15] = 128;

DataEncrypted[16] = 149;

DataEncrypted[17] = 67;

DataEncrypted[18] = 187;

DataEncrypted[19] = 111;

DataEncrypted[20] = 192;

DataEncrypted[21] = 70;

DataEncrypted[22] = 250;

DataEncrypted[23] = 136;

DataEncrypted[24] = 58;

DataEncrypted[25] = 148;

DataEncrypted[26] = 70;

DataEncrypted[27] = 184;

DataEncrypted[28] = 46;

DataEncrypted[29] = 71;

DataEncrypted[30] = 209;

DataEncrypted[31] = 45;

aesCTX.mIvSize = 16;

aesCTX.mKeySize = 32;

aesCTX.mFlags = E_SK_DEFAULT;

aeserror = AES_CBC_Decrypt_Init(&aesCTX, (uint8_t*)KeyTemp, (uint8_t*)KeyIvTemp);

aeserror = AES_CBC_Decrypt_Append(&aesCTX,(uint8_t*)DataEncrypted,32,DataRaw,&aesoutputsize);

aeserror = AES_CBC_Decrypt_Finish(&aesCTX,(uint8_t*)DataRaw,&aesoutputsize);

The decryption only works for the first 16 bytes, fails for the next 16 bytes. The following website shows what the decryption should be 

http://aes.online-domain-tools.com/link/eea909ghxsatKRjSA/

.

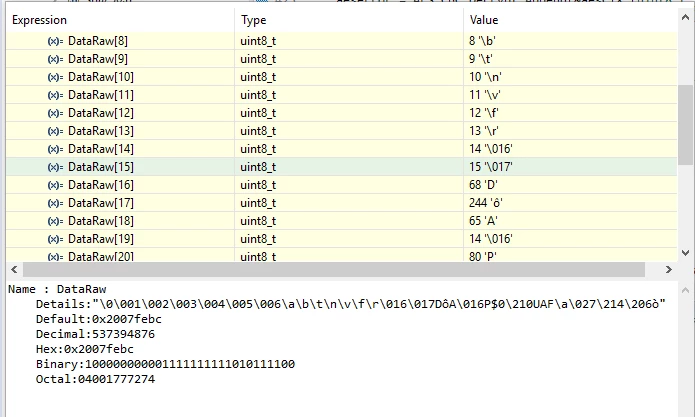
This is what i get when i run it.

0690X00000608apQAA.png

Which is wrong since the plaintext goes from 0-31.

Anyone know what im doing wrong?

-Andriy

    This topic has been closed for replies.
    Best answer by Tesla DeLorean
    Posted on October 13, 2017 at 05:51

    DataEncrypted[18] = 187; // This should be 184

    7 replies

    Tesla DeLorean
    Guru
    October 12, 2017
    Posted on October 13, 2017 at 00:31

    For ST code make sure the clock is enabled on the CRC Peripheral, it is how they lock the libraries to the STM32 parts.

     __CRC_CLK_ENABLE (); 

    I'll take a look at the data a bit later..

    Tips, Buy me a coffee, or three.. PayPal Venmo (See Profile) Up vote any posts that you find helpful, it shows what's working..
    Tesla DeLorean
    Guru
    October 13, 2017
    Posted on October 13, 2017 at 02:38

    >>

    Encryption on host is done correctly, ...

    I'm not convinced, show how you did it.

    Your input data is flawed, using entirely different AES-256 code I get

    0000 : 00 01 02 03 04 05 06 07-08 09 0A 0B 0C 0D 0E 0F ................

    0010 : 44 F4 41 0E 50 24 30 88-55 41 46 07 17 8C 86 F2 D.A.P$0.UAF.....
    Tips, Buy me a coffee, or three.. PayPal Venmo (See Profile) Up vote any posts that you find helpful, it shows what's working..
    ayarema
    ayaremaAuthor
    Associate II
    October 13, 2017
    Posted on October 13, 2017 at 04:51

    I have studied the CBC mode and why IV is needed. The keys and values im using arent random so i can see it work.

    Encryption was done in C# and since the first 16 bytes were decrypted correctly that must mean the rest were also encrypted correctly. Also this(

    /external-link.jspa?url=http%3A%2F%2Faes.online-domain-tools.com%2Flink%2Feea909ghxsatKRjSA%2F

    ) site is an online AES decryptor and when i feed in those keys with the ciphertext i get exactly what i expect as the decrypted data. This leads me to believe the issue is somehow on the MCU decryption side.

    If you want to try replicate what im doing here is the C# code:

    AesManaged myAes = new AesManaged();

    byte[] IV = new byte[16];

    byte[] key = new byte[32];

    byte[] plaintext = new byte[32];

    byte[] ciphertext = new byte[32];

    for(int i = 0; i < 32; i++)

    {

    key[i] = (byte)i;

    plaintext[i] = (byte)i;

    if(i < 16)

    {

    IV[i] = (byte)i;

    }

    }

    myAes.Mode = CipherMode.CBC;

    myAes.IV = IV;

    myAes.Key = key;

    myAes.Padding = PaddingMode.None;

    // Create a encryption object to perform the stream transform.

    ICryptoTransform encryptor = myAes.CreateEncryptor();

    encryptor.TransformBlock(plaintext, 0, 32, ciphertext, 0);

    And hereare the values of the ciphertext at the end of executing the above:

    0690X00000608b9QAA.png

    Also side note tried _CRC_CLK_ENABLE(); right after the rest of the initialization no difference.

    -Andriy