

dming.4
Associate II
Oct 25, 2019 11:03 AM UTC
Solved

Why stm32f2 bootloader check application always failed?

Hello:

I use this to check the address is application in stm32f207VET6.

void go2APP(void) {
 uint32_t JumpAddress;
 pFunction Jump_To_Application;
 
 //Check
 if (((*(__IO uint32_t*) FLASH_APP_ADDR) & 0x2FFE0000) == 0x20000000) {
 printf("APP Start...\n");
 HAL_Delay(100);
 // Jump to user application //
 JumpAddress = *(__IO uint32_t*) (FLASH_APP_ADDR + 4);
 Jump_To_Application = (pFunction) JumpAddress;
 // Initialize user application's Stack Pointer //
 __set_MSP(*(__IO uint32_t*) FLASH_APP_ADDR);
 Jump_To_Application();
 } else {
	 printf("No APP found!!!\n");
 }
}

When i erase the whole chip i get this
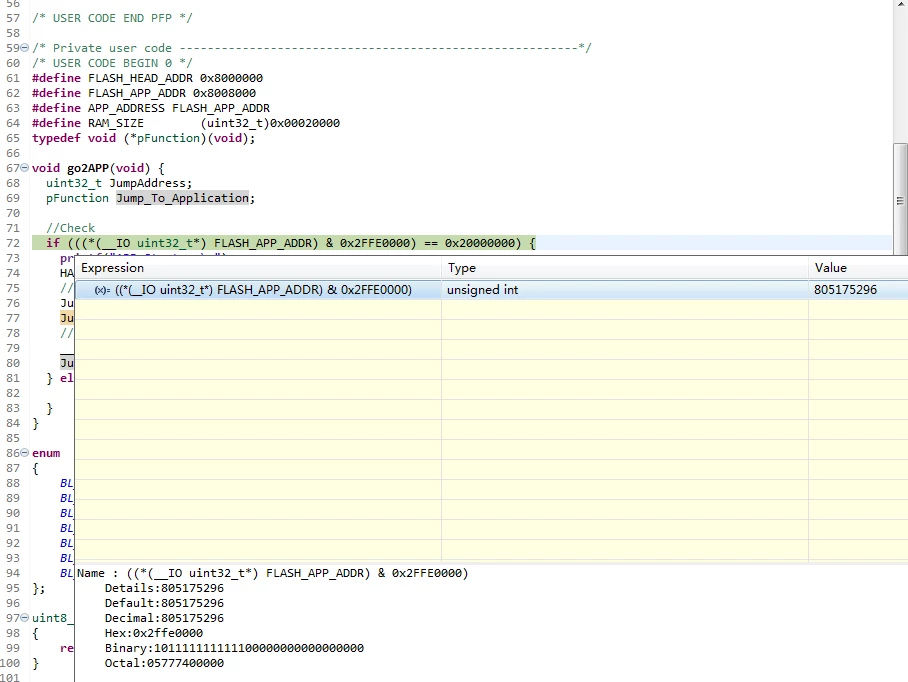
 0690X00000AqsOzQAJ.png

But when i use jflash to program an application hex to the application address

I get this
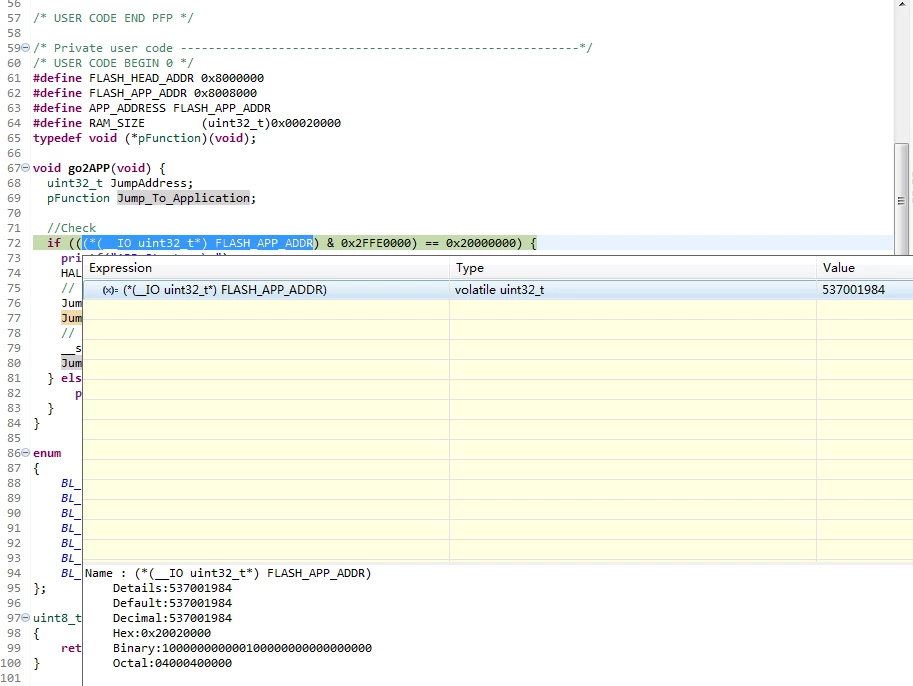
0690X00000AqsOBQAZ.png

Even i use the flash base address to check but also get 0x20020000 .

Should i change the 0x2FFE0000 to 0x2FFD0000 ?

Thank you
This topic has been closed for replies.
Tesla DeLorean
Tesla DeLoreanBest answer
Guru
Oct 25, 2019 2:42 PM UTC

Perhaps just mask with 0xFFF00003, all the test is doing is ensuring that the stack pointer is in RAM, it is a crude test, and perhaps a hold-over from parts with smaller memories. Keil doesn't place it at the end of memory, but at the end of the allotted space the linker knows about. GNU/GCC typically places it at the top-of-RAM, but a lot of ST scripts are defective and use an unaligned address. The address pre-decrements, so you can park it just beyond, ie for 128KB system you use 0x20020000, and not 0x2001FFFF

Tips, Buy me a coffee, or three.. PayPal Venmo (See Profile) Up vote any posts that you find helpful, it shows what's working..

5 replies

TDK
Oct 25, 2019 1:57 PM UTC

Why do you think that check should pass?

If you’re trying to test if it’s something other than 0xFFFFFFFF just do that instead.

"If you feel a post has answered your question, please click ""Accept as Solution""."
dming.4
dming.4Author
Associate II
Oct 25, 2019 2:40 PM UTC

you should see the second picture before you type something.

My question is why i flash the application to the 0x8008000 but could not pass the check.

TDK
Oct 25, 2019 2:44 PM UTC
Okay, good luck.
"If you feel a post has answered your question, please click ""Accept as Solution""."
dming.4
dming.4Author
Associate II
Oct 25, 2019 2:40 PM UTC

/

Tesla DeLorean
Tesla DeLoreanBest answer
Guru
Oct 25, 2019 2:42 PM UTC

Perhaps just mask with 0xFFF00003, all the test is doing is ensuring that the stack pointer is in RAM, it is a crude test, and perhaps a hold-over from parts with smaller memories. Keil doesn't place it at the end of memory, but at the end of the allotted space the linker knows about. GNU/GCC typically places it at the top-of-RAM, but a lot of ST scripts are defective and use an unaligned address. The address pre-decrements, so you can park it just beyond, ie for 128KB system you use 0x20020000, and not 0x2001FFFF

Tips, Buy me a coffee, or three.. PayPal Venmo (See Profile) Up vote any posts that you find helpful, it shows what's working..