

H563zi Trustzone dual bank Flash user
Hello everyone,
I'm testing the use of trustzones in my application. The examples are working fine, however my application requires more FLASH in the non-secure zone than in the secure zone. The initial examples have the following parameters (default):
The memory definition in the secure linker script is as follows:
/* Memories definition - Secure Zone  */
MEMORY
{
  RAM    (xrw)    : ORIGIN = 0x30000000,   LENGTH = 320K
  FLASH    (rx)    : ORIGIN = 0x0C000000,   LENGTH = 1016K
  FLASH_NSC    (rx)    : ORIGIN = 0x0C0FE000,   LENGTH = 8K
}
The memory definition in the non-secure linker script is as follows:
/* Memories definition - Non-Secure Zone */
MEMORY
{
  RAM    (xrw)    : ORIGIN = 0x20050000,   LENGTH = 320K
  FLASH    (rx)    : ORIGIN = 0x08100000,   LENGTH = 1024K
}
The Option bytes is as follows:
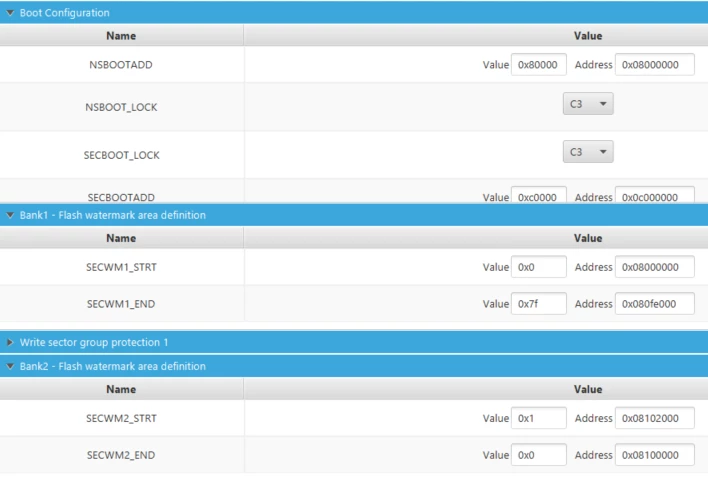
So far it works. My application requires me to use 80K of memory in the secure zone and 1968K of memory in the non-secure zone, as I will show below:
The memory definition in the secure linker script is as follows:
/* Memories definition - Secure Zone  */
MEMORY
{
  RAM    (xrw)    : ORIGIN = 0x30000000,   LENGTH = 320K
  FLASH    (rx)    : ORIGIN = 0x0C000000,   LENGTH = 72K
  FLASH_NSC    (rx)    : ORIGIN = 0x0C012000,   LENGTH = 8K
}
The memory definition in the non-secure linker script is as follows:
/* Memories definition - Non-Secure Zone */
MEMORY
{
  RAM    (xrw)    : ORIGIN = 0x20050000,   LENGTH = 320K
  FLASH    (rx)    : ORIGIN = 0x08014000,   LENGTH = 1968K
}
The Option bytes is as follows:
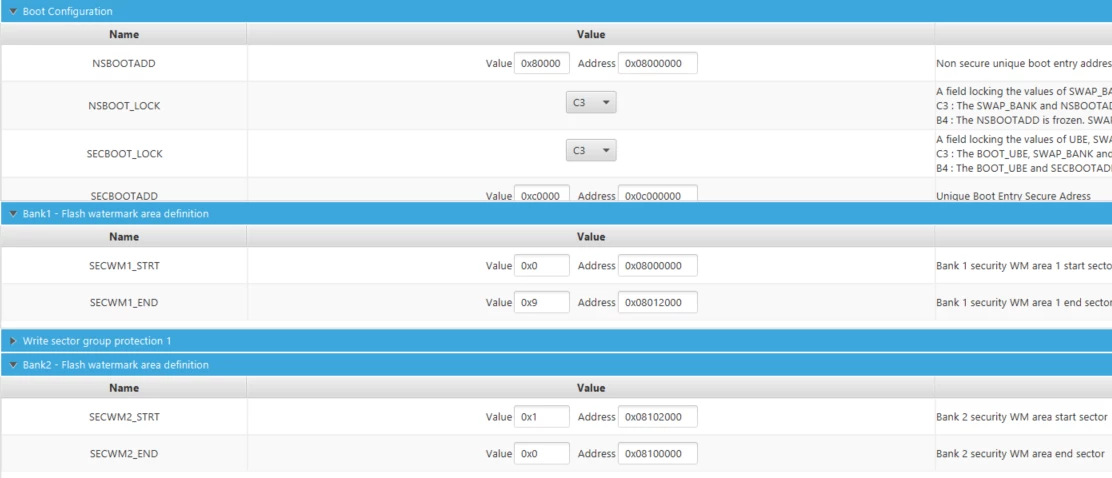
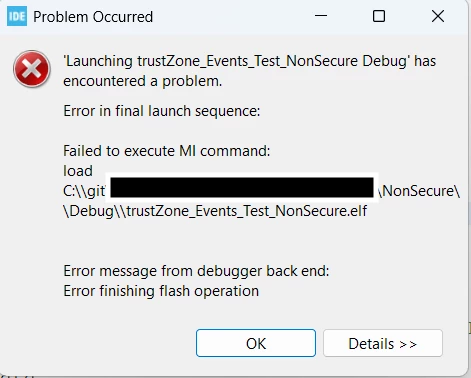
And when I try to run the application I get this error:
I'd like to know where I'm going wrong, and also ask a question: if I define the range of safe and unsafe FLASH in option bytes, would it be necessary to modify the linker?